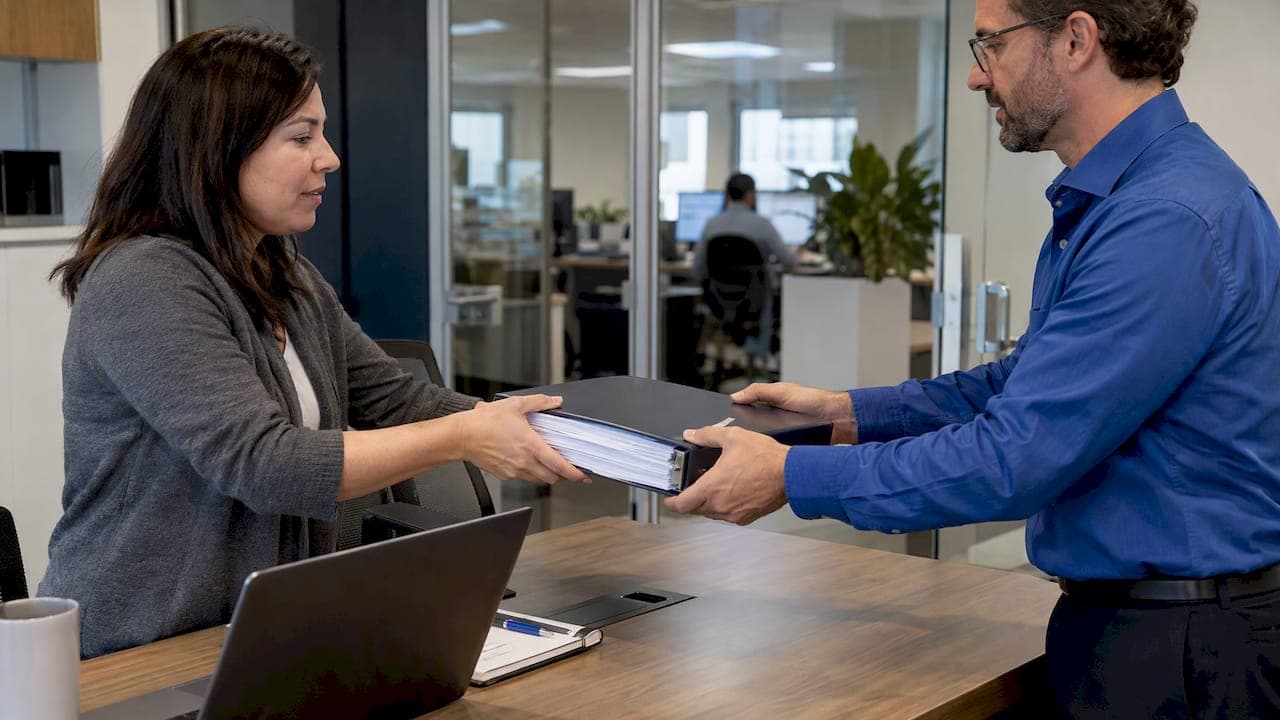
A complete clinical vendor handoff transfers the work plus the context, authority, and verifiable evidence, so the receiving team can act without rebuilding the story. That is the single test: can they use the deliverable without delay? Handing over files is not enough. We at HaiPhai work as an operational partner for teams that want this done right.
TL;DR:
- Attach each deliverable’s version history, named owners, unresolved items with owners and due dates, record inventory, acceptance evidence, and required next steps.
- Set acceptance criteria before work moves, inventory and freeze the source, then test results and secure written acceptance before revoking outgoing access.
- The sponsor retains ultimate accountability, so assign transition leads on both sides and record every decision, owner, evidence reference, and escalation trigger.
- Acceptance tests should examine underlying records, audit trails with counts and timestamps, and reconciliations across systems; use checksum comparisons when available.
- For vendors handling regulated data or network access, scale security reviews to risk, grant only necessary access for a defined period, and document its removal.
Table of Contents
- What belongs on a minimum handoff checklist?
- How do you run a handoff step by step?
- Who stays responsible, and how should governance work?
- What evidence makes data and records trustworthy?
- Which security and onboarding checks should be part of the handoff?
- Which templates and artifacts should travel with every handoff?
- What small habits prevent the most common handoff failures?
- Why do handoffs look clean on paper and fail in practice?
- How does an operational partnership close the gaps?
- FAQ
- Sources
What belongs on a minimum handoff checklist?
A handoff that arrives as a folder and a cheerful email is a handoff that will be reconstructed later, usually under inspection pressure. A complete handoff identifies the deliverable, version, owner, known gaps, assumptions, related decisions, downstream users, required follow-up, and supporting evidence. On-time delivery alone does not prove anyone is in control. Attach this minimum set to every handoff:
- Identity and history: the deliverable name, current version, and change history, so nobody works from a stale copy.
- Named owners: one person on the sending side and one on the receiving side, with contact details.
- Open items: known gaps, assumptions, and unresolved decisions, each with an owner and a due date.
- Record inventory: documents, data, configurations, credentials, training records, and contracts, listed so nothing is assumed to travel on its own.
- Acceptance evidence: reconciliation reports, audit-trail exports, eTMF or document-quality review results, and the signed acceptance.
- Follow-up terms: required actions, escalation points, and the SLA or acceptance timeframe.
If a field cannot be filled in, write that down rather than leaving it blank. A documented gap with an owner is manageable. A silent one is how a missing protocol deviation log surfaces later.
How do you run a handoff step by step?
The order matters more than the speed. A reliable sequence follows the transition pattern described in federal sponsor-transfer rules, where documents, data, and responsibilities are inventoried and accepted rather than simply passed along.
- Define the trigger and decision authority. Say what starts the handoff (a contract end, a vendor swap, a scope change) and who can approve it.
- Set acceptance criteria up front. Agree on what "done" looks like before any work moves.
- Inventory and freeze the source. List documents, data, configurations, credentials, training records, contracts, and open issues, then freeze or version-control the source environment.
- Transfer knowledge and access. Run structured walkthroughs, then grant the receiving team access.
- Run reconciliation and acceptance tests. Capture the results, not just a statement that they passed.
- Obtain written acceptance. Revoke outgoing access, then start monitoring for continuity.
Pro Tip: Schedule the acceptance tests before the walkthroughs. Teams that know what they will be tested on ask better questions during knowledge transfer.
Who stays responsible, and how should governance work?
Sponsors do. Sponsors retain ultimate responsibility for outsourced activities, and vendor oversight should be risk-based, backed by SOPs, SLAs, and governance aligned to a Quality Management System. Delegating a task is not the same as delegating accountability.
- Assign roles explicitly. Use a RASCI matrix and name a transition lead on each side, with escalation thresholds written down.
- Make owners visible. Every open issue and decision needs a named person, not a department.
- Show evidence, not mood. A governance review should present the decision, its owner, and the supporting evidence. A status panel of green, amber, and red tells you how people feel, not whether the handoff is usable.
- Escalate on triggers. Define in advance what delay or gap forces a sponsor-level decision.
If a meeting ends without a recorded decision, owner, and evidence reference, it was a briefing, not governance.
What evidence makes data and records trustworthy?
A summary report is not transferable evidence. Receiving teams need access to the underlying records so they can verify what they are inheriting.
- Audit-trail exports with metadata: include record counts and timestamps. Summaries hide the very discrepancies an inspector looks for.
- Reconciliation checks: compare record counts and reconcile timestamps between sending and receiving systems. Where tooling supports it, add hash or checksum comparisons.
- Chain of custody and provenance: for lab or imaging transfers, document who handled what and when. Independent lab verification is a useful model, as this guide to third-party testing shows for labs, tests, and proof.
- Cross-validation on platform change: when methods or platforms change, bridge the old and new results rather than assuming they match.
Build these checks into the acceptance test script so passing them is required, not optional.
Which security and onboarding checks should be part of the handoff?
When a vendor touches regulated data or your network, security artifacts belong in the acceptance package. One documented example: Mayo Clinic's supplier onboarding reviews policies, attestations, and process documents, and includes annual external security assessments and penetration tests for suppliers, with onboarding depth mapped to supplier category. That is one institution's case study, not a universal rule, so scale it to your risk.
- Document the artifacts: policy attestations, process documents, and penetration test reports where applicable.
- Limit access: time-bound, least-privilege permissions for every vendor account.
- Prove revocation: include confirmation that outgoing access was removed in the signed acceptance evidence.
- Match depth to risk: require external assessments for high-risk supplier categories and lighter checks elsewhere.
For a deeper walk-through of qualification, see our vendor qualification workflow.
Which templates and artifacts should travel with every handoff?
Repeatable templates cut review time and make inspection readiness a habit rather than a scramble.
- Handoff inventory spreadsheet: every record, owner, version, and location in one place.
- Acceptance test script: the tests, expected results, and space for actual results.
- Signed acceptance form: who accepted what, and when.
- Open-issues tracker: each item with an owner and a due date.
Store all of it in a governed central repository such as the eTMF or a data warehouse, under version control. If your team is building an inspection-facing process, our inspection readiness sprint shows how to organize it.
What small habits prevent the most common handoff failures?
- Name leads on both sides: hold short, frequent check-ins until acceptance is signed.
- Test against real records: require sample access to underlying data during acceptance, not just summaries.
- Standardize governance output: always decision, owner, evidence.
Pro Tip: Keep the open-issues tracker in the same repository as the acceptance form, so no one can sign off without seeing what remains open.
Why do handoffs look clean on paper and fail in practice?
I call it the handoff illusion, and Applied Clinical Trials describes the same trap: vendors can own defined scopes, but contracts do not automatically own the interfaces, cross-vendor dependencies, or escalation paths between them. Passive delegation hides that risk until it lands downstream. The fix is active facilitation by the sponsor, and for recurring or high-risk handoffs, an embedded partner who does that work daily is worth considering. Our operating partnership and AI Velocity Diagnostic exist for exactly that case.
— John
How does an operational partnership close the gaps?
Most handoff failures trace back to the same three gaps: an incomplete checklist, governance that reports status instead of decisions, and evidence nobody verified. We embed senior expert teams inside your operations, map where work stalls, and redesign workflows around your regulatory and scientific needs, with continuous governance after go-live. If you want to see where your handoffs leak time, start with our operating partnership and AI Velocity Diagnostic and book a conversation with us.
FAQ
What is a handoff in healthcare?
A handoff is the transfer of essential information and responsibility from one party to another. Ineffective handoffs create patient-safety and adverse-event risk, and the literature recommends standardized communication tools such as SBAR and templates to improve them.
What is the role of a vendor in a clinical trial?
A vendor performs a defined scope of outsourced work for the sponsor, such as data management, imaging, or patient-reported outcomes. The sponsor keeps ultimate responsibility, so vendor work still needs risk-based oversight, SLAs, and clear acceptance criteria.
How do I choose among clinical vendors?
Start with the category of work and the risk it carries, then match onboarding depth to that risk. Our guide to choosing eCOA vendors shows how this applies to one common category.
What should a handoff acceptance record include?
It should include the deliverable and version, the named owners, reconciliation and audit-trail evidence, open issues with owners, access-revocation confirmation, and the signed acceptance. If the receiving team cannot use the deliverable without reconstructing context, the handoff is not complete.
Sources
- Why Vendor Oversight Breaks Down At Handoffs
- Law
- Csrc
- Vendor Selection and Management
- The Handoff Illusion: Why Clean Transitions in Clinical Development Are a Myth